Permissions
Permissions in Typograph are resource-scoped. Every action checks the role you hold on the specific resource you're touching — team, project, or template — not a single global role per user.
How Permissions Are Granted
- Joining an organization gives you an organization role (owner, admin, member). This controls organization-wide administration only.
- Being invited to a team, project, or template gives you a resource role (owner, editor, commenter, viewer) on that resource. It inherits to children of that resource — e.g. an editor on a project can edit templates in that project.
Permission Model
At a glance:
| Capability | Owner | Editor | Commenter | Viewer |
|---|---|---|---|---|
| View contents | ✓ | ✓ | ✓ | ✓ |
| Comment | ✓ | ✓ | ✓ | |
| Edit content | ✓ | ✓ | ||
| Invite others | ✓ | ✓ | ||
| Change roles | ✓ | |||
| Delete / move to trash | ✓ |
(Exact capabilities are maintained by the Identity Service and may expand over time. The Portal always reflects live configuration.)
Organization-Only Capabilities
These aren't controlled by resource roles — only by organization role:
| Capability | Owner | Admin | Member |
|---|---|---|---|
| View org members | ✓ | ✓ | ✓ |
| Invite org members | ✓ | ✓ | |
| Change a member's role or remove them | ✓ | ✓ (not the owner) | |
| Manage OAuth apps | ✓ | ✓ | |
| Manage webhooks | ✓ | ✓ | |
| Let the apps of guests read, and block one | ✓ | ✓ | |
| Change subscription | ✓ | ||
| Delete organization | ✓ |
Sharing a Resource
- Open the team, project, or template.
- Click Invite.
- Enter email, pick a role.
- The invitee receives an invite — once accepted, the resource shows up under Shared with me.
Only the address the invite was sent to can accept it. Opening the link while signed in with another account shows which address the invite went to (partly hidden, like j•••@example.com) and a Switch account button: sign in with the right account and you land back on the invite.
An invite to a team gives access to everything in that team. An invite to a specific project or template limits access to just that scope.
Can edit and Admin each take one of your plan's editor seats, once per person; viewing and commenting is free. When the seats are all taken, the dialog turns both off: see Invites → Editor seats.
Which Role Counts
Someone can hold a role on a team and another on a project or template in it. The role closest to what they open counts, also when it is lower: an editor of the team can be given Can comment on one project, and then comments there while editing everything else in the team.
An admin is the exception: whoever is admin of a team stays admin of every project and template in it, and an admin of a project stays admin of every template in it. Giving them less there would change nothing, so Typograph refuses it:
- Inviting them to a project or template with a role below Admin is refused, naming their address: they are admin of the team or project it is in, and stay admin here. Invite them as Admin, or leave their access as it is.
- In the Share dialog, their row reads Admin through the team or Admin through the project, without a role to pick.
- An invitation for less, sent before they became admin above, says so when they open it, and cannot be accepted: ignore it.
Accepting an invitation for less than you can do now, as an editor of the team invited to comment on one project, is allowed: the invitation page says what you can do already, and that accepting gives you the lower role there instead.
Your Own Access
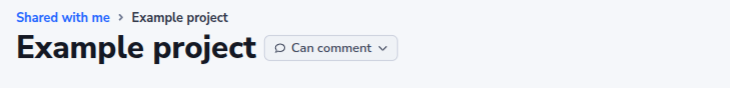
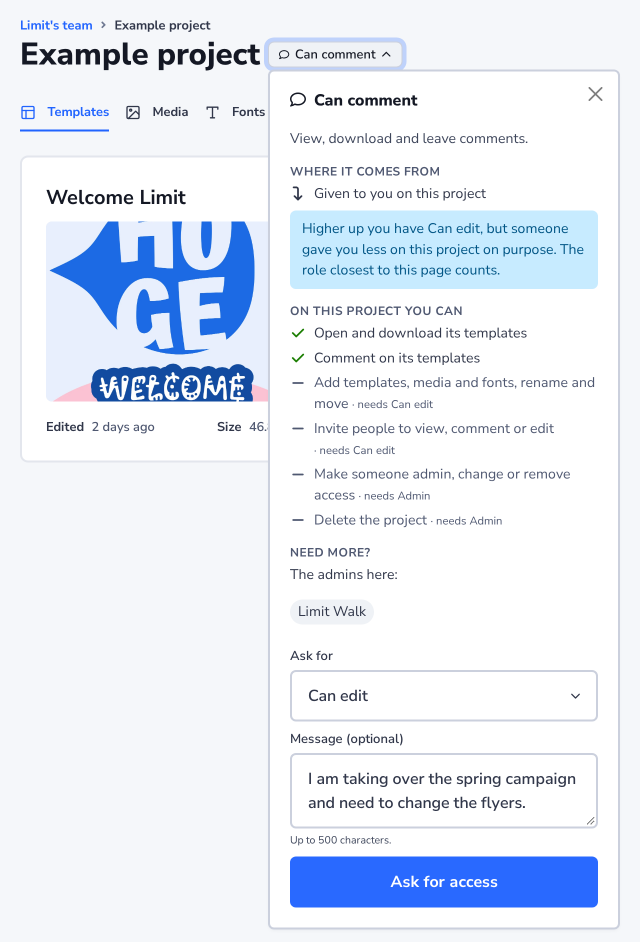
Every team, project and template shows your role beside its title: Can view, Can comment, Can edit or Admin. In the editor it sits in the bar above the design. A role that ends says until when: Can view · until 12 Dec.
Click it to see what your role means there:
- Your role, in the words the Share dialog uses: Can comment is "View, download and leave comments".
- Where it comes from: Through the team Marketing, with a link to it, when it comes with the team or project it is in. When it was given on this page itself, it says Given to you on this project. When your role ends, it says when, and what you keep after that.
- Set lower here: if you can do more in the team or project above, but were given less here on purpose, the panel says so, and what you get back once a role that ends has ended. The role closest to what you open counts (see Which Role Counts).
- What you can do here: six lines, from opening it to deleting it. What your role does not give you is greyed out with a minus and the role it takes, so you also see what a higher role would let you do.
- Need more?: the admins here, by name, and a form to ask them for a higher role (see Asking for Access). Someone who shares only a project sees the admins of that project, never those of the team they are not in. An admin has nothing more to ask for, so their panel ends above it.
Press Escape, click the cross or click outside the panel to close it. On a phone the panel opens as a sheet at the bottom of the screen; tap above it to close it.
Under Shared with me, each card shows your role on it in the same words.
Asking for Access
When your role is not enough, ask the admins for more from the label beside the title:
- Click your role, such as Can view, beside the title of the team, project or template.
- Under Need more?, pick the role you need in Ask for: only the roles above yours are offered, Can comment, Can edit or Admin.
- Optionally, under Message (optional), tell the admins what you need it for, in up to 500 characters.
- Click Ask for access.
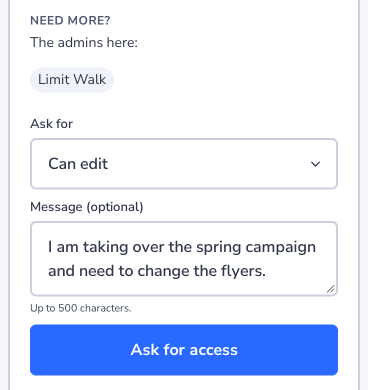
The admins of the team, project or template get a notification; when it has none, the admins of the project or team it is in do. The panel now says what you asked for, such as "You asked for Can edit. The admins have been told, and you get a notification when they answer." Open it later and it says when you asked.
You get a notification with the answer: the role you were given, which may differ from the one you asked for, or that your request was declined. A request nobody answers within 30 days lapses, and you are told that too; you can ask again.
You can have one request open per team, project or template. To ask for another role, click Withdraw request in the same panel, then ask again. You can have at most 20 requests open at once.
You can only ask where you can open the team, project or template already. To get into something you cannot see at all, ask the person who works on it to invite you.
Answering Requests for Access
Whoever can share a team, project or template sees the requests for it in its Share dialog, under Asking for access, above Who has access. The notification about a request links to the page it is about, where you open Share.
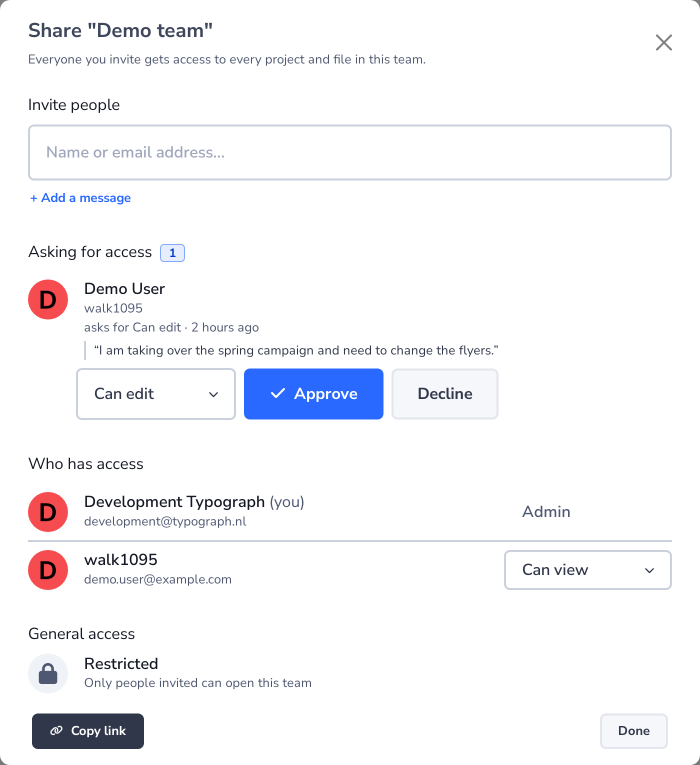
Each request shows who asks, for which role and how long ago (asks for Can edit · 2 hours ago), and their message, if they wrote one. To answer it:
- Approve gives them the role in the list beside it. It starts at the role they asked for; pick another to give more or less. They get that role on this team, project or template itself, and Who has access shows it at once.
- Decline turns the request down.
Either way the request leaves the list and they get a notification.
Who can answer which request:
- Can edit answers requests for Can comment and Can edit from people who have no role on this page itself yet, such as someone who sees it through the team.
- Admin answers every request, including those for Admin and those of people whose role was set on this page, also when it was set lower on purpose.
A request you cannot answer is not listed for you. Giving Can edit or Admin takes one of your plan's editor seats, as an invite does; when they are all taken, approving says so, and you can give Can comment instead (see Invites → Editor seats).
Seeing Who Has Access
The Share dialog of a project or template lists under Who has access everyone who can open it. People who have access because they are in the team (for a project) or in the project and its team (for a template) are grouped in one row: Everyone in the team or project, via the team or via the project, with how many people that is.
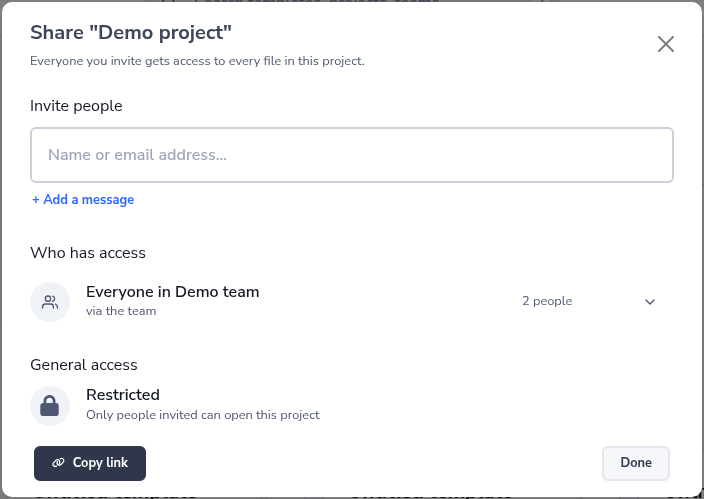
Click that row to see who they are. It opens to list each person, with their email address and the role they have there; click it again to close it.
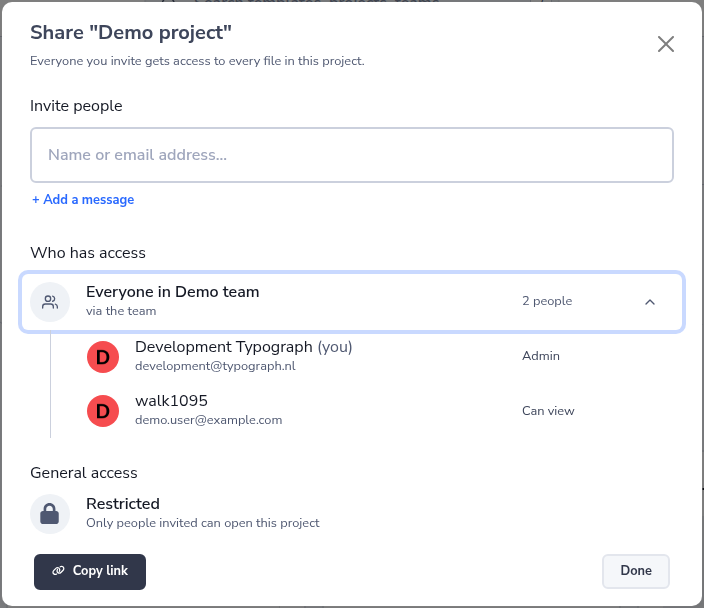
The list is for reading only. To add someone to the team or project, or to change or remove their role, open the team or project itself and use its Share dialog. Someone who is in a project but not in its team sees, in a template's dialog, the project's own people and a note that others have access through the team. In the project's own dialog they see the team's row with how many people are in it; opened, it says that only people in the team can see who is in it.
Revoking Access
Open the resource's Share dialog and remove the user, or change their role. On a project page, the faces next to Share show the first four people with access; when there are more, the count after them (+3) opens the same dialog with everyone. Removal is immediate — their next request fails with a 403.
API Parity
The same permission checks apply over the REST API. Token scopes (file:read, file:write, file:delete) gate the categories of operations, and resource-role checks gate the specific resources the token can touch. See API → Token Types and API → Scopes.
Related
- Roles — the role catalog
- API → File Service — invites, roles, permissions and requests for access